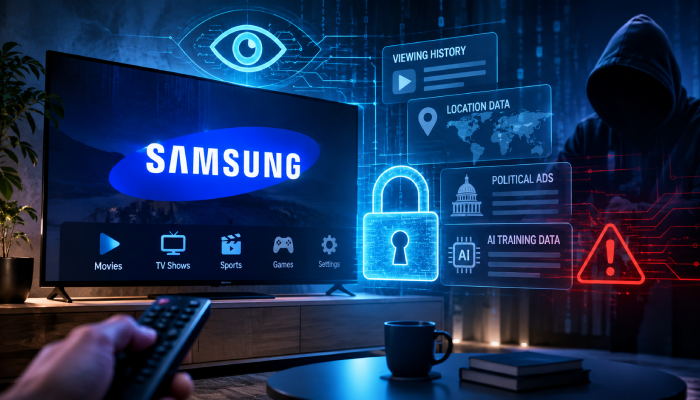
The alleged exposure of 150,000 Samsung smart TV viewing records, political advertising information and AI training data highlights the growing risks of connected devices, behavioural tracking and the expanding commercial data ecosystem.
“Privacy cannot remain an afterthought in the connected-device economy. Manufacturers must take responsibility for the entire lifecycle of consumer data, from collection and processing to storage, sharing and eventual deletion.”
A television was once a passive household appliance. Today, it is an internet-connected computing platform, an advertising channel and a sophisticated data collection endpoint. The alleged data breach involving Samsung Electronics has brought this transformation under renewed scrutiny, raising serious questions about how much information smart televisions collect, where that information travels and how effectively it is protected.
According to an investigation published by Cybernews on November 19, 2026, the ransomware group n0n claims to have stolen and leaked approximately 220MB of data belonging to Samsung. The material was reportedly published on the group’s dark web leak site after an extortion countdown expired.
Researchers examining the exposed files identified approximately 150,000 smart TV viewing events, 42,600 political advertising records and 99,100 records associated with AI advertising model training. The files also reportedly contained internal documents revealing employee information and details about Samsung’s data infrastructure.
Although Samsung had not commented on the allegations at the time of the report, the incident raises a much larger question for the technology industry: has the rapid expansion of connected-device intelligence outpaced the security and privacy frameworks designed to protect consumers?
The television becomes a data collection platform
Modern smart televisions are no longer simply devices for displaying entertainment. They integrate streaming applications, voice assistants, recommendation engines, internet connectivity and personalised advertising services.
These capabilities create convenience, but they also generate substantial amounts of data.
Depending on device configurations, user permissions and service settings, smart televisions can collect information about application usage, viewing activity, advertising interactions, device characteristics and network connectivity. This information may be transmitted to cloud platforms for analytics, content recommendations and advertising purposes.
The Samsung incident illustrates the potential scale of this information ecosystem.
According to Cybernews, the largest exposed dataset contains approximately 150,000 viewing events recorded during 2024. The records reportedly include timestamps, viewing durations, device information, cities, ZIP codes and television service provider names.
The researchers did not report that the dataset identified the specific programmes watched by individual users. Nevertheless, the exposed information provides insights into viewing patterns and device usage.
This distinction is important. Personal information does not always need to contain a person’s name, email address or telephone number to become sensitive.
When timestamps, geographical information and device characteristics are combined, they can potentially reveal household routines, consumption patterns and behavioural trends. If correlated with other datasets, such information could become considerably more revealing.
The television in a living room may therefore be generating a digital footprint with significant commercial value.
The political advertising connection
One of the more intriguing aspects of the alleged exposure is the discovery of approximately 42,600 records associated with political advertising campaigns between September and October 2026.
According to Cybernews, the records contain political affiliations, issues discussed in advertisements, sponsors, estimated advertising expenditure and timestamps. The exposed material also reportedly includes a political advertisement video.
This brings another dimension of the connected television ecosystem into focus: the intersection of digital advertising, political communication and behavioural data.
Traditional television advertising has relied largely on programme ratings, audience demographics and geographical markets. Connected television platforms can offer advertisers more sophisticated targeting and campaign measurement capabilities.
This creates commercial opportunities, but also introduces concerns about transparency and accountability.
Political advertising data can reveal campaign priorities, sponsorship arrangements, expenditure patterns and the issues receiving promotional attention. If exposed, such information could provide insights into political communication strategies.
The broader concern is the growing concentration of information within advertising technology ecosystems. Manufacturers, advertising platforms, analytics providers and external partners may all participate in processing information generated by connected devices.
Each additional integration introduces another relationship that needs to be governed and secured.
AI advertising models: The next data security challenge
The reported exposure of approximately 99,100 records associated with AI advertising model training adds another important dimension to the incident.
Cybernews researchers found that this dataset primarily consists of embedding vectors, mathematical representations used by machine learning systems to identify relationships and similarities between information.
Embeddings are fundamental to modern AI applications. They help systems organise information, identify patterns and support recommendation, classification and retrieval processes.
In advertising ecosystems, these representations can support audience segmentation, personalised recommendations and predictive targeting.
Their exposure does not automatically mean that the original training material or individual identities can be reconstructed. However, depending on how the embeddings are generated and stored, they may present inference and information-disclosure risks.
This raises an important question for organisations investing in AI-driven advertising: are their training datasets, model artefacts and supporting infrastructure receiving the same security attention as conventional customer databases?
AI governance discussions often concentrate on model accuracy, bias, transparency and regulatory compliance. Protecting data throughout the AI lifecycle deserves equal attention.
Training datasets, embedding repositories, model checkpoints and inference logs must be classified, monitored and protected through appropriate access controls.
As AI becomes increasingly integrated into customer engagement and advertising, securing the model ecosystem becomes inseparable from protecting consumer privacy.
“Every connected device is becoming a data collection point. The real challenge is ensuring that the information generated by these devices does not become a liability for consumers and businesses.”
Third-party data sharing expands the attack surface
Modern connected television platforms do not operate independently. They interact with streaming services, advertising technology companies, analytics providers and cloud infrastructure operators.
This interconnected environment makes data governance increasingly complicated.
Consumers may purchase a television from one manufacturer, use applications from multiple service providers and receive advertisements delivered through several intermediaries. Yet they may have little visibility into the complete journey of their information.
For manufacturers, this creates a shared-responsibility challenge.
Even when primary infrastructure is adequately protected, vulnerabilities in partner environments, improperly configured data warehouses or compromised employee credentials can expose information beyond the original organisation’s security perimeter.
Third-party risk management must therefore move beyond contractual assurances.
Organisations need to establish what information is collected, which external parties receive it, how long it is retained, whether appropriate consent exists and how access is monitored.
The objective should be to minimise unnecessary data collection and sharing rather than simply securing an ever-expanding pool of information.
Ransomware evolves into data extortion
The alleged Samsung incident also highlights the changing business model of ransomware groups.
Traditional ransomware operations focused on encrypting systems and demanding payment for restoring access. Attackers subsequently recognised that stolen information could create an additional source of leverage.
The double-extortion model combines data theft with the threat of public disclosure. Even organisations with effective backups can face considerable reputational, regulatory and commercial consequences when sensitive information is published.
Cybernews identifies n0n as a relatively new ransomware operation that attracted attention in September 2026. The group has reportedly listed prominent organisations, including Visa, Mastercard, Walmart, JPMorgan and Starbucks, among its alleged victims. It has also reportedly leaked data associated with Expedia.
These claims should be distinguished from independently verified compromises. A listing on a ransomware leak site does not, by itself, establish the authenticity or completeness of the material.
Research by cybersecurity firm SOCRadar, cited by Cybernews, also describes the group’s use of generative AI to assist reconnaissance and scripting activities.
This reflects a broader shift in the threat landscape. Generative AI can reduce the time and technical effort required to develop scripts, automate routine activities and process information gathered during reconnaissance.
For defenders, this means that security strategies must account for faster reconnaissance, automated attack preparation and increasingly frequent data extortion attempts.
Identity protection, continuous monitoring, data access governance and incident response readiness are becoming essential.
What CISOs and CIOs should learn from the incident
Although the alleged breach involves consumer electronics, its implications extend to enterprise security.
Smart televisions, digital displays, surveillance systems, conference room equipment and other connected appliances are increasingly integrated into corporate environments.
In hotels, hospitals, educational institutions and offices, these devices may connect to corporate Wi-Fi, digital signage platforms and cloud-based management systems.
An inadequately secured connected device can become a potential entry point into a wider environment.
CIOs and CISOs should consider five priorities:
1. Establish connected-device visibility: Maintain an inventory of smart televisions, IoT devices and other connected equipment, including their firmware versions, network connections and associated cloud services.
2. Implement network segmentation: Keep entertainment and guest-facing devices separate from sensitive corporate networks through dedicated VLANs and restricted communication policies.
3. Strengthen identity security: Enforce multi-factor authentication, privileged access controls, credential rotation and regular reviews of third-party access.
4. Monitor data movement: Deploy appropriate data loss prevention, endpoint detection and response, network monitoring and cloud security controls to identify suspicious transfers.
5. Secure AI and third-party ecosystems: Extend security assessments to advertising platforms, AI service providers, analytics systems, training datasets and model repositories.
The objective is to identify unauthorised access and data movement before information appears on public leak sites.
The regulatory dimension: Privacy must become a business priority
The alleged Samsung data exposure comes at a time when digital privacy and data protection are receiving greater regulatory attention.
In India, the Digital Personal Data Protection Act, 2023, and the Digital Personal Data Protection Rules, 2025, provide a framework governing the processing of digital personal data. Organisations must understand their applicable obligations based on the nature of the information, their role in processing it and the relevant commencement provisions.
Not every technical record necessarily qualifies as personal data. However, information that can be linked to an identifiable individual may attract data protection requirements depending on the circumstances.
For technology manufacturers operating across multiple markets, compliance becomes even more complex. They must navigate different privacy regimes, consent requirements, data transfer restrictions and breach notification obligations.
However, regulatory compliance alone cannot solve the underlying problem.
Organisations need to move towards privacy-by-design, where data minimisation, security and accountability are embedded into product development and operational processes.
What consumers should do
Smart television owners do not necessarily need to abandon connected devices, but they should understand the information these products may collect.
Consumers should review privacy and advertising settings, examine Automated Content Recognition options, disable non-essential tracking where possible and regularly install firmware updates.
They should also review application permissions, secure associated accounts, change default passwords and consider connecting smart televisions to a separate guest or IoT network.
Disabling personalised advertising does not necessarily stop all device telemetry or service-related data collection. The actual effect depends on the manufacturer’s policies and device configuration.
The emphasis should therefore be on informed usage rather than assuming that a single privacy setting eliminates all tracking.
The bigger question: Who owns the data generated by our devices?
The alleged Samsung leak highlights a fundamental contradiction in the connected-device economy.
Consumers purchase televisions, smartphones, smart speakers and other appliances to make everyday life more convenient. Manufacturers monetise these ecosystems through subscriptions, analytics, services and advertising.
But the information generated through these interactions can become valuable far beyond its original purpose.
The viewing records reportedly exposed in the Samsung incident demonstrate how ordinary device activity can become part of a larger commercial data infrastructure. The political advertising records raise questions about transparency in digital campaigning, while the AI training records highlight the growing importance of protecting machine learning assets.
These are different categories of information, but they point towards the same underlying weakness: data collection and sharing are expanding faster than the governance and security arrangements surrounding them.
The industry must recognise that collecting information for commercial purposes creates responsibilities that extend beyond obtaining user consent.
Manufacturers need to establish clear boundaries around what they collect, how long they retain it, with whom they share it and how they protect it.
Data minimisation should become a business principle rather than merely a regulatory obligation. The less unnecessary information an organisation collects and retains, the smaller the potential consequences of a breach.
The future of connected technology will not be determined solely by smarter screens, better recommendations or more personalised experiences. It will also depend on whether manufacturers can earn and maintain consumer trust.
The television in the living room may not be watching in the human sense. But it can generate a surprisingly detailed digital footprint of a household.
And when that footprint travels across interconnected advertising, analytics and AI platforms, protecting it becomes a responsibility that extends far beyond the device manufacturer.
Editorial note: This feature is based on the Cybernews investigation published November 19, 2026. The alleged 220MB leak, exposed datasets and attribution to the n0n ransomware group require independent verification. Samsung had not publicly responded to the allegations at the time of the report. The quotations at the beginning are editorial pull quotes, not statements attributed to Samsung or any named spokesperson.